Chrome HTTP Warning Since 21 October 2026: Why Your Campaign Visitors May Bounce and a Checklist for Egyptian Websites
Short answer: Since 21 October 2026, Google Chrome asks users for permission before opening any public site that does not work over HTTPS, and the warning appears on the first visit, which means in front of the new visitor arriving from an ad, a QR code or an old link. Chrome accounts for about 80% of browsing in Egypt, so every Egyptian business should make sure its bare domain, its www version and every redirect step work with a valid certificate.
The Chrome HTTP warning is an interstitial page that Google Chrome shows before connecting to a public site over unencrypted HTTP, asking the user to either go back or continue. In this article we explain what changed, why it affects marketing before it affects security, what we found when we tested 332 Egyptian domains, and a practical checklist for website owners, clinics and online stores in Egypt.
What is the Chrome HTTP warning (Ask-before-HTTP)?
Chrome now tries to open every link over HTTPS first. If a secure connection is not possible and the browser believes the site may work over HTTP, it shows a warning asking the user before continuing. Google describes the change in its official announcement of 21 October 2026 as enabling the "Always Use Secure Connections" setting for all users by default, after it had been limited earlier in the year to users enrolled in Enhanced Protection in Safe Browsing.
The key points about how the warning works:
- It appears on the first visit: once the user approves, the warning does not repeat for that site. Chrome remembers the decision for 15 days and renews it on every visit, according to the Chromium guide for website owners, while Google's blog describes the period as two weeks.
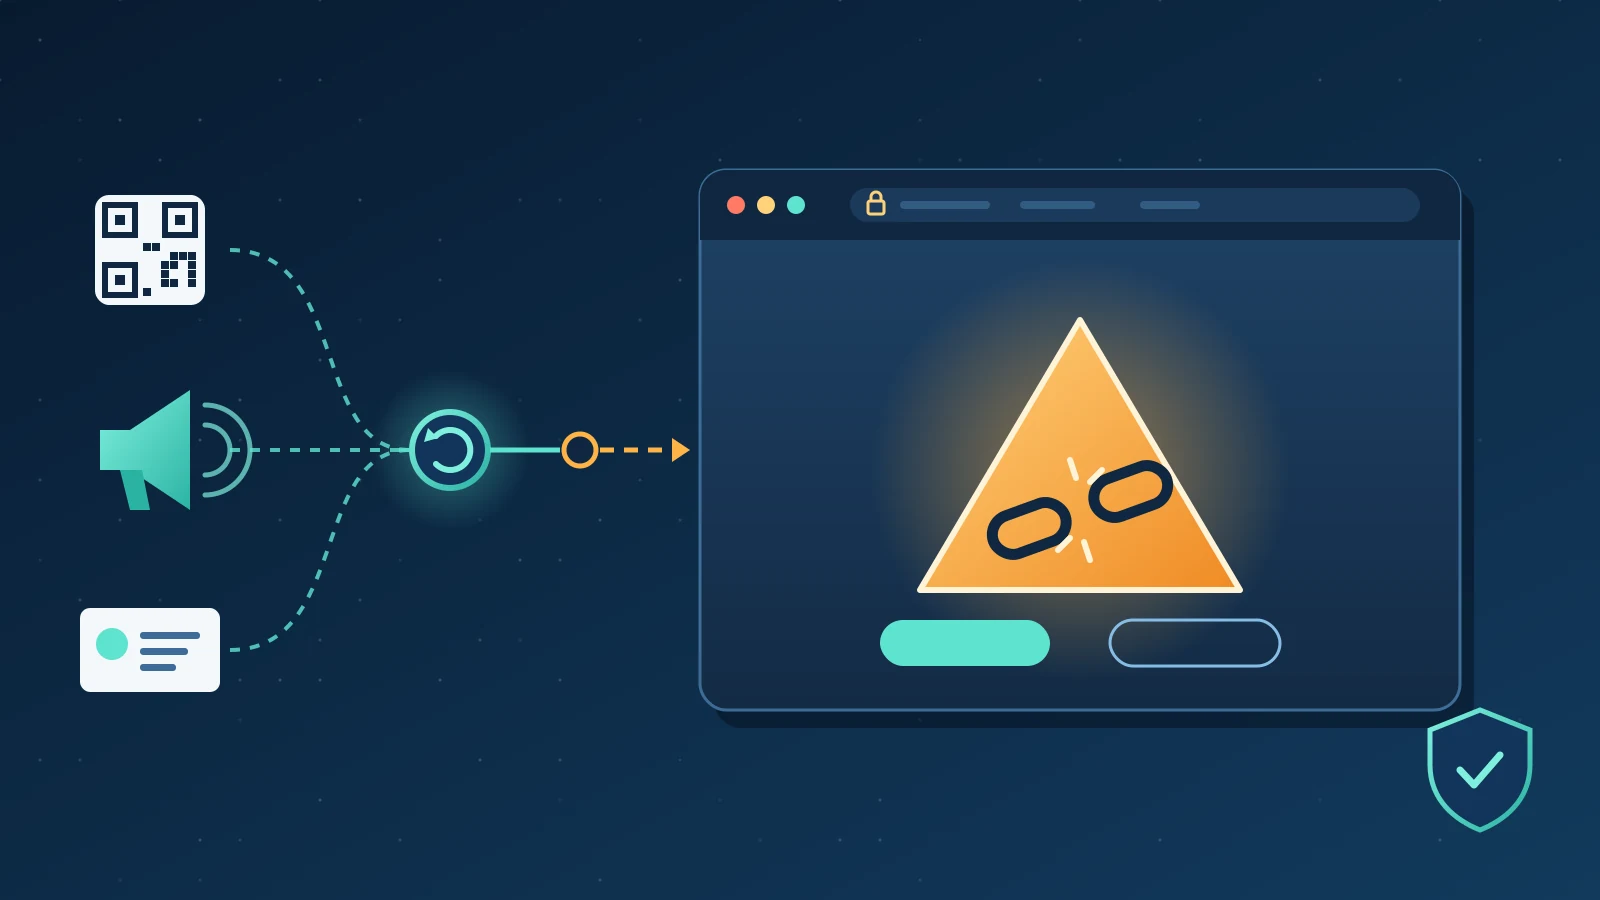
- It covers redirect steps: if the visitor passes through a single HTTP step in a redirect chain before reaching an HTTPS page, the warning appears even though the final page is secure.
- It excludes private networks: by default it does not appear on local IP addresses such as 192.168.0.1, single-label names such as intranet/, or localhost.
- HSTS prevents fallback to HTTP: for sites that send the Strict-Transport-Security header, Chrome does not try HTTP at all.
Timeline of the change
| Date | What happened | Source |
|---|---|---|
| 2022 | "Always Use Secure Connections" launched as an opt-in setting | Google blog, 28 October 2025 |
| Chrome 141 | Default-on experiment for a small percentage of users: the median user saw fewer than one warning per week | Google blog, 28 October 2025 |
| 28 October 2025 | Announcement of default enablement with Chrome 154 in October 2026 | Google blog |
| April 2026 (Chrome 147) | Enabled for more than 1 billion users enrolled in Enhanced Safe Browsing | Google blog, 28 October 2025 |
| 21 October 2026 | Enabled for all users by default | Google blog, 21 October 2026 |
In its 28 October 2025 announcement, Google says the share of Chrome navigations over HTTPS climbed from around 30-45% in 2015 to the 95-99% range around 2020 and then largely plateaued, and that this plateau is what pushed it to go beyond the "Not Secure" badge.
Why the Chrome HTTP warning matters for the Egyptian market
According to StatCounter's figures for Egypt, Chrome held 80.29% of browsing in September 2026, followed by Safari at 8.96% and Edge at 3.42%. In other words, any HTTPS misconfiguration on your website will be visible to most of your Egyptian audience.
The most important marketing point is that the warning is designed to appear for new visitors, or for those who have not visited for a while. That is exactly the visitor you pay for: someone who clicked a paid ad, scanned a QR code on a clinic sign, or opened the link from a business card or a printed brochure. A returning customer may have approved once and forgotten, but a prospect sees a warning page before seeing your offer, and may simply press "Back".
Google says nearly 95% of Chrome desktop users do not see any HTTP warning in a given week, and less than 1% see three or more. The warning has become rare, so a website that triggers it will stand out as an exception rather than a normal occurrence.
What we found when testing 332 Egyptian domains
On 24 October 2026 the Smart One Group team ran its own test on every .eg domain in the Tranco top one million list (that day's list), 332 domains in total. For each one we checked the bare name and the www version, 664 hostnames, over HTTPS with strict certificate validation.
| Result | Count |
|---|---|
| Domains where at least one name responded over HTTPS with a valid certificate | 252 |
| Domains where both the bare name and www work with a valid certificate | 199 |
| Domains where one name has a valid certificate and the other a mismatched or expired one | 13 |
| Domains with at least one name whose certificate does not match the hostname | 16 |
| Domains with an expired certificate | 4 |
| Domains whose bare name sends an HSTS header, out of 217 whose bare name worked over HTTPS in the first pass | 70 |
The practical takeaway: the most common mistake we saw is a certificate that covers www.example.com.eg but not example.com.eg, or the reverse. Egyptian visitors often type the bare name, and designers often print it without www, so the secure connection fails on the uncovered name. Also, only about a third of working sites (70 of 217) enable HSTS on the bare name.
Methodology note: the test ran from a single vantage point outside Egyptian networks, port 80 (HTTP) could not be tested from our test environment, and we excluded 137 hostnames whose attempts ended in an inconclusive timeout or reset. The results are a preliminary estimate and do not name individual websites.
Where HTTP hides in your marketing campaigns
In Egyptian companies, HTTP rarely lives on the website itself. It lives in the entry points that lead to it:
- Printed QR codes on signs, prescriptions and product boxes that carry http:// or a name not covered by the certificate.
- Business cards and brochures that print the bare name without www.
- The website field in Google Business Profile and social media pages set up years ago.
- Campaign tracking links and URL shorteners that pass through an HTTP step.
- Registrar domain forwarding of an old .com.eg or .eg domain to a new site without a certificate.
- Email signatures and old links on directories and partner websites.
That is why we recommend making a link check a fixed step before launching any campaign as part of your digital marketing plan, and before printing any material that carries a QR code.
The Smart One Group framework: five stations of a secure visitor journey
This is Smart One Group's own working framework that we use with our clients, not a standard issued by Google:
- Inventory entry points: collect every link to your site in ads, print, QR codes, profiles and signatures in one sheet.
- Name coverage: make sure the certificate covers the bare name, www and every subdomain in use, and that every additional domain you own (such as .com and .com.eg) has a certificate.
- Redirect chain: every step must be HTTPS, and the best redirect goes from https://example.com.eg straight to the final address in a single hop.
- Enable HSTS once stable: start with a short duration and increase it after confirming every subdomain works over HTTPS.
- Monitoring and renewal: monitor certificate expiry and enable automatic renewal, especially as SSL certificate validity is being cut step by step.
How to test your website in 30 minutes
- Enable "Always Use Secure Connections" at chrome://settings/security, as the Chromium guide recommends.
- Type your bare domain in the address bar without http or www, then repeat with www.
- Open the Network panel in DevTools and check every redirect step to confirm it is HTTPS.
- Scan your printed QR codes with a phone running Chrome, and try your ad links and Google Business Profile link.
- If a warning appears, note the hostname it shows and fix it with your hosting provider or registrar.
If your site is on hosting that does not issue certificates automatically, or your domain is forwarded through a service that does not support HTTPS, this is a good time to review your hosting plan and domain management.
Notes for companies that manage employee devices
Internal systems on local IP addresses or single-label names will not show the warning by default. Systems published on public names over HTTP, such as an old admin panel on a subdomain, will. Chrome offers organizations the HttpAllowlist policy to exempt specific sites and the HttpsOnlyMode policy to enforce the setting, including the force_balanced_enabled value. The better fix, however, is moving those systems to HTTPS, which we handle as part of our technical support contracts.
Frequently asked questions
Does the Chrome warning block visitors from my website?
No, the warning can be bypassed and the user can continue. But it puts an extra step in front of new visitors that may make them leave, especially if they came from a paid ad.
My site runs on HTTPS, so am I safe?
Not necessarily. If the bare name or www is not covered by the certificate, or if there is an HTTP redirect step, visitors may see the warning even though the final page is secure.
Does the warning appear on mobile?
Yes. Google enabled the setting for all users by default, and Android Authority reported that it applies on both desktop and mobile. Google says warning rates on mobile are even lower than on desktop.
Does the warning affect internal company systems?
It does not appear by default on local IP addresses and single-label names, but it does appear on systems published on public domains over HTTP.
How often will a visitor see the warning?
Once, on the first visit. Chrome then keeps the approval for 15 days, renewed with each visit. If the visitor stays away longer, the warning returns.
Is the old "Not Secure" badge enough to spot the problem?
No. The badge does not appear during short redirect steps. The reliable method is to enable the setting, test every entry point and review the redirect chain.
If you would like us to review the visitor journey to your website, from the ad or QR code to the final page, and fix certificates and redirects without disrupting your campaigns, we would be glad to hear from you through the Smart One Group contact page.